
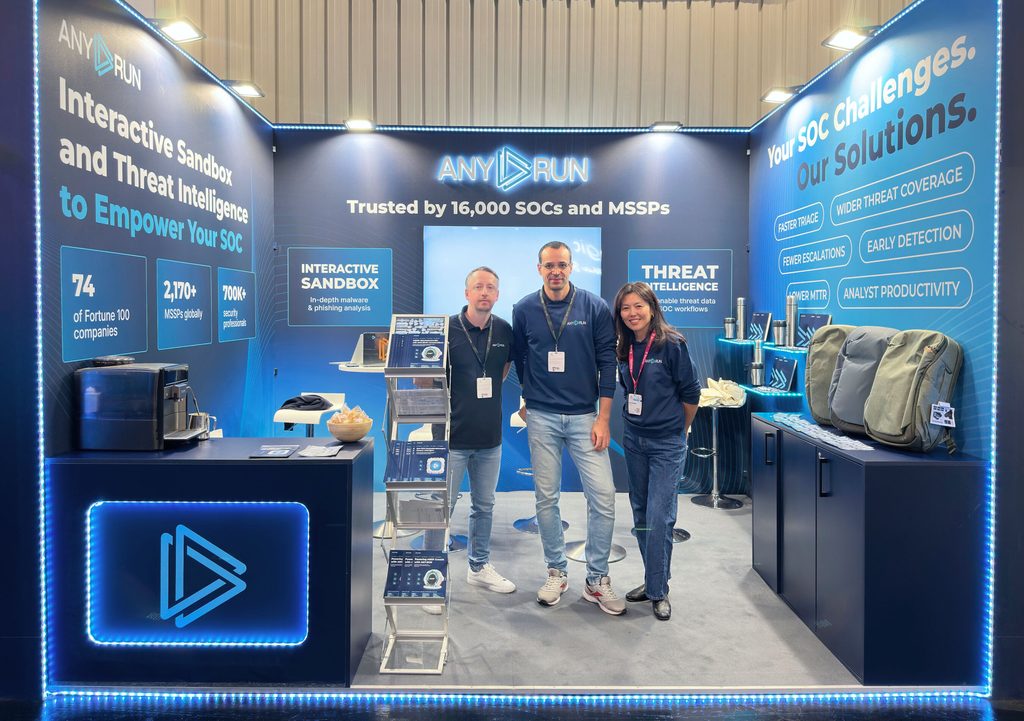
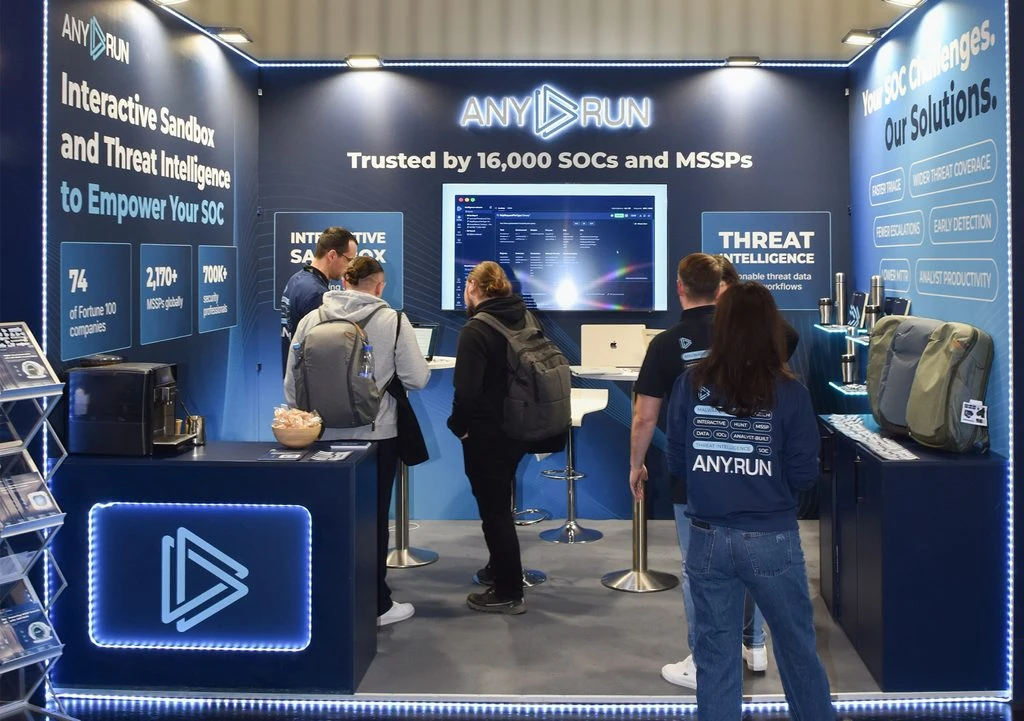
From October 27 to 29, the ANY.RUN team joined it-sa 2026 in Nuremberg, meeting customers, partners, SOC and MSSP teams, and cybersecurity professionals from across Europe.
Three days of conversations gave us a valuable opportunity to hear what security teams are focused on today, exchange ideas about evolving security operations, and discuss how malware analysis and threat intelligence can support faster and more confident decisions.
Meeting Customers and the Cybersecurity Community
This year, visitors could meet ANY.RUN at two locations: our booth in Hall 9, Stand 9-114, and in Hall 6, Stand 6-432 together with ALLNET GmbH.
It was great to reconnect with existing customers, meet new organizations, and speak directly with security professionals working with malware, phishing, incident response, and threat intelligence every day.
Many conversations focused on practical challenges familiar to modern SOC and MSSP teams:
- Reducing time spent validating suspicious files and URLs;
- Giving analysts stronger evidence for incident response decisions;
- Using fresh threat intelligence to support investigation and threat hunting;
- Improving detection against new and changing threats;
- Building security processes that meet growing enterprise and regulatory requirements.
These conversations are especially valuable because they connect technology with the reality of day-to-day security operations. They also give our team direct insight into the priorities, constraints, and workflows that security teams are dealing with across different industries and environments.
DORA, NIS2, and Security Compliance Were Part of the Conversation
Compliance and operational resilience were also recurring topics at it-sa.
For organizations operating in Europe, frameworks such as DORA and NIS2 continue to influence how security teams approach ICT risk, incident handling, supply-chain security, operational resilience, and relationships with technology providers.
As a result, organizations evaluating cybersecurity solutions increasingly look beyond individual technical capabilities. The security controls of the provider, protection of sensitive information, and the ability to support controlled enterprise workflows are also part of the discussion.
ANY.RUN has achieved SOC 2 Type II attestation and ISO 27001 certification, independently validating the controls and information security management practices behind our malware analysis and threat intelligence services.
For organizations with strict internal security and vendor requirements, these standards provide additional assurance when integrating ANY.RUN into investigation and threat intelligence workflows.
From Faster Triage and Response to Stronger Security Operations
A key topic in our conversations at it-sa was how SOC and MSSP teams can improve the entire security operations workflow, from detecting suspicious activity to validating threats, investigating incidents, and strengthening future detection.
Reducing manual work at each stage is essential to keeping investigations moving. When analysts spend too much time validating alerts, collecting indicators, or rebuilding investigation context, response decisions take longer and unnecessary escalations consume senior analysts’ time.
ANY.RUN helps teams address these challenges through connected malware analysis and threat intelligence workflows.
Validate Threats Faster and Improve Escalation Decisions
At the triage stage, ANY.RUN’s Interactive Sandbox helps analysts quickly examine suspicious files and URLs, observe malicious behavior, and collect evidence for a confident verdict.
This allows Tier 1 analysts to resolve more cases with sufficient evidence and escalate those that genuinely require deeper investigation.
The operational impact is measurable: 94% of ANY.RUN users report faster triage, while SOC workflows using ANY.RUN have demonstrated 30% fewer Tier 1 to Tier 2 escalations.
Accelerate Investigations and Response
When an alert requires deeper investigation, analysts need to understand the threat, identify related activity, and determine the potential incident scope without repeating earlier research.
ANY.RUN Threat Intelligence Lookup helps teams investigate indicators, uncover related infrastructure, and connect behavioral findings with broader threat context.
Together, behavioral analysis and threat intelligence support faster investigation decisions and clearer handoffs between SOC tiers.
Across ANY.RUN-supported workflows, 95% of SOCs report faster threat investigations, with a reported 21-minute improvement in Mean Time to Respond.
Turn Investigation Findings into Earlier Detection
The value of an investigation extends beyond resolving the immediate incident. Confirmed malicious indicators and newly identified infrastructure can also help security teams improve future monitoring.
ANY.RUN Threat Intelligence Feeds help operationalize fresh indicators in existing security systems, supporting earlier detection and reducing the need for repeated manual checks.
For SOCs, this creates a continuous process where investigation findings contribute to stronger detection. For MSSPs, it supports consistent investigation practices, better escalation quality, and more efficient security operations across customer environments.
Thank You for Meeting Us at it-sa 2026
it-sa 2026 was another great opportunity to meet the people behind the security teams we work with every day.
Thank you to everyone who stopped by our booths, shared their experience, asked questions, discussed their security challenges, or simply came to say hello. We also want to thank ALLNET GmbH for joining us at the event.
Conversations like these help us stay close to the real operational needs of SOCs, MSSPs, threat hunters, and incident response teams.
We look forward to meeting the cybersecurity community again at the next event.
About ANY.RUN
ANY.RUN helps security teams improve malware and phishing analysis across triage, investigation, incident response, threat hunting, and detection engineering.
Its Interactive Sandbox and Threat Intelligence solutions are used by more than 700,000 security professionals and 16,000 organizations worldwide. ANY.RUN has achieved SOC 2 Type II attestation and ISO 27001 certification, supporting enterprise requirements for information security and data protection.
Want to discuss how ANY.RUN can fit into your security operations? Contact our team.