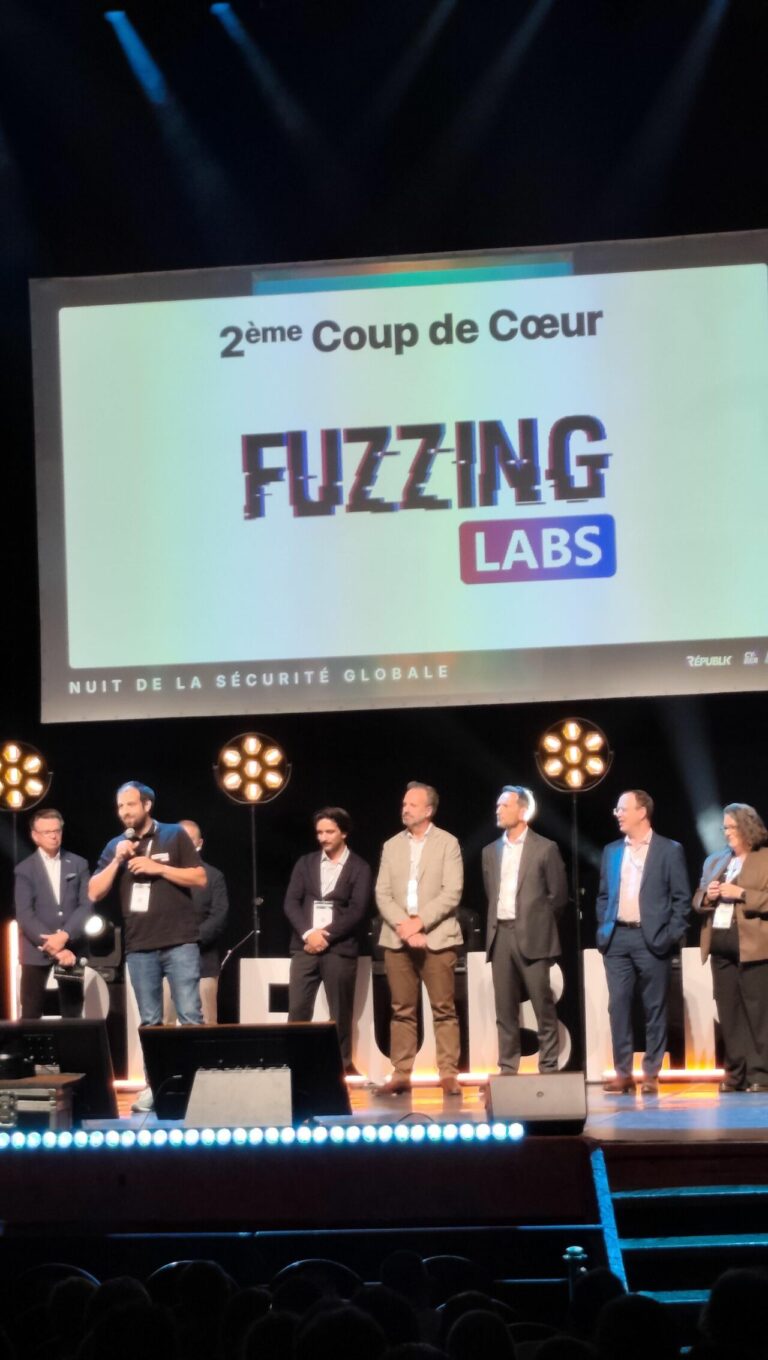
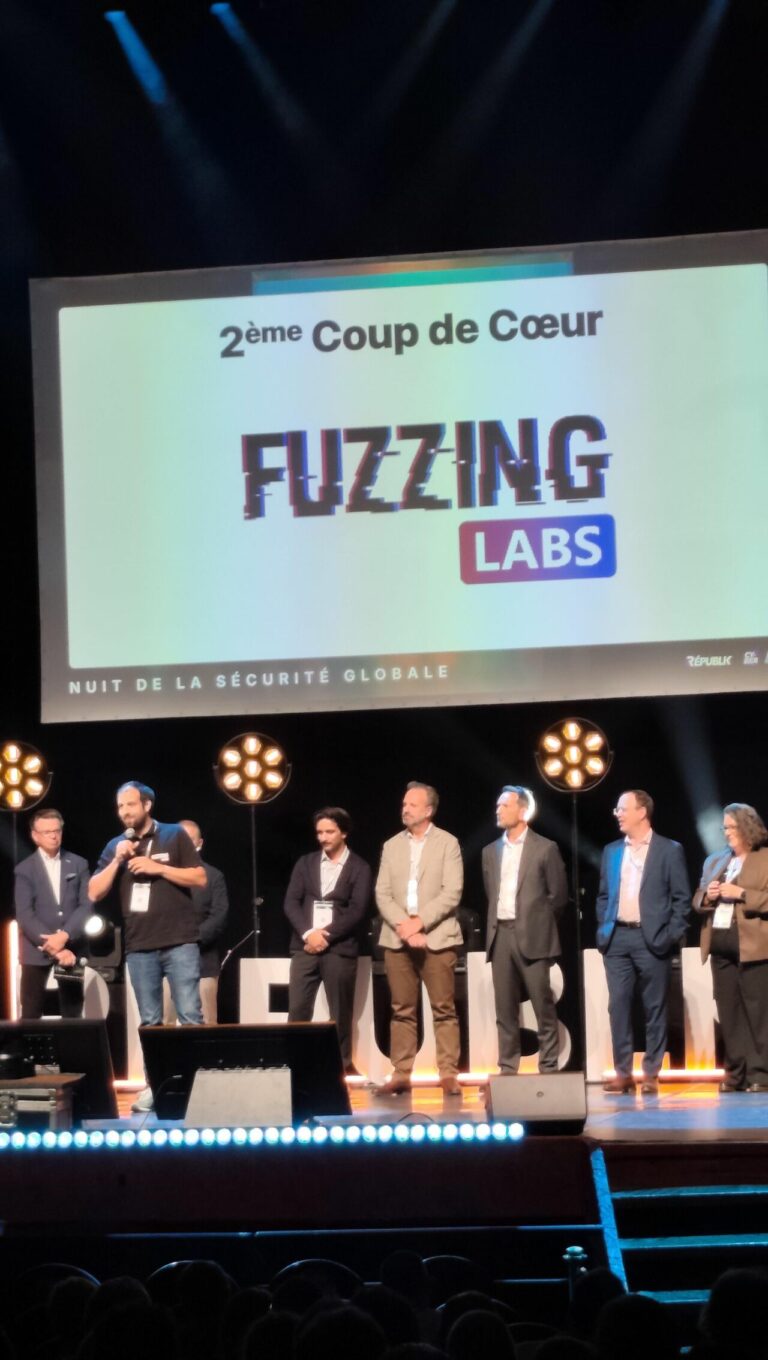
On 28 September 2026, FuzzingLabs received the 2nd Coup de Cœur in the Innovative cyber suppliers category at the Nuit de la Sécurité Globale 2026, at the Théâtre Mogador in Paris. The award recognises our work on a blind spot of cybersecurity: continuous offensive security for binaries and embedded systems. That is the core of FuzzForge.
What is the Nuit de la Sécurité Globale?
It is the annual awards ceremony of the French security and safety sector, organised by Républik Group. Its roots go back to the Trophées de la Sécurité, created in 2007.
The 2026 edition in a few facts:
- Around 800 professionals in the room.
- 80 candidates competing for the awards.
- A grand oral in early September: 3 minutes to pitch, 3 minutes of questions.
- A jury of security directors from large companies, scoring innovation, effectiveness, sustainability and the quality of the presentation.
That last point is why this award matters to us. The people who judged FuzzForge are the people who buy security.
What did the jury reward?
The jury rewarded FuzzForge, our platform for continuous security and compliance validation of connected and embedded products.
In practice, FuzzForge tests the software inside these products, even without the source code. It runs fuzzing, emulation and reverse engineering at scale, on-premise and sovereign.
Why is embedded software a security blind spot?
Because the software that runs critical systems is the hardest to test, and the least tested. Three reasons come up in every conversation we have with product security teams:
| Problem | What it means in practice |
|---|---|
| Tooling | Binaries ship without source code. Classic tools are not built for them. |
| Expertise | Researchers who can analyse embedded software are rare. Hiring does not close the gap. |
| Pace | Products ship updates continuously. A yearly audit is outdated the day it ends. |
You hand over a firmware image or a binary. Specialised AI agents take it apart, and you get findings you can verify.
- Add your firmware and binaries. No source code needed.
- Let the agents attack. Fuzzing, emulation and reverse engineering, orchestrated at scale.
- Get proven findings. Each candidate is challenged before it is reported, false positives are filtered out, and every bug is replayable.
The platform can run where your code already lives: SaaS, private cloud, on-premise, or air-gapped with local models only. Your code does not have to leave your perimeter.
See how FuzzForge works, or how it helps defense and government programs.
Who sits on the jury?
Security and safety directors from large companies. They assess candidates on innovation, effectiveness, sustainability and presentation.
What is FuzzForge?
A platform for continuous security and compliance validation of connected and embedded products, built by FuzzingLabs.
Patrick Ventuzelo, CEO & Founder of FuzzingLabs·LinkedIn
FuzzingLabs was founded in 2021 by Patrick Ventuzelo, a vulnerability researcher who spent more than ten years finding the flaws hidden in firmware and binaries. He built FuzzingLabs to turn that passion into a company, and to teach it.
Today, FuzzingLabs is a French team of researchers and engineers. They compete at Pwn2Own, present at Black Hat and OffensiveCon, and pour that same passion into FuzzForge, the platform at the heart of the company.