Reporting period: 22–29 September 2026Collection cutoff: 29 September 2026, ~1100 EDTExecuti 2026-9-29 16:7:50 Author: krypt3ia.wordpress.com(查看原文) 阅读量:5 收藏
Reporting period: 22–29 September 2026
Collection cutoff: 29 September 2026, ~1100 EDT
Executive assessment
The strongest development this week is further confirmation that Russia’s European covert-action campaign is targeting the defense-industrial and Ukraine-support ecosystem, with espionage/reconnaissance feeding physical sabotage. Estonia today formally attributed the August arson attack against Milrem Robotics, which supplies unmanned ground vehicles to Ukraine, to Russian security services. Three Latvian nationals were arrested. This is significant because the target fits the same Russian collection requirement previously visible around British drone factories, German defense companies, Romanian surveillance of Ukrainian aviation, and cyber collection against drone technology. AP News
A second major development concerns supply-chain and trusted-vendor access. DOJ alleges that digital-forensics vendor Oxygen Forensics concealed continued Russian ownership and Russian software development while selling sensitive forensic technology to the Pentagon and several DHS components, including the U.S. Secret Service. Critically, DOJ does not allege malware, unauthorized access, or an intelligence operation. The case nevertheless represents a serious counterintelligence exposure because the Russian sister company sold the same technology to the FSB and other Russian security bodies. Justice Department
Third, New Zealand’s NCSC now identifies the PRC as its most persistent and capable state-backed cyber threat, with China, Russia, Iran, and North Korea all linked to activity against New Zealand. Twenty-three percent of nationally significant cyber incidents handled in 2025–26 had suspected state-sponsored links. NCSC New Zealand
Key judgment: Russia currently shows the clearest movement from collection → target development → proxy recruitment → sabotage. China continues to emphasize persistent strategic access and information acquisition. Iran continues to demonstrate that inexpensive online recruitment can generate real-world surveillance and logistics capabilities.
Estonia’s Internal Security Service, KAPO, announced on September 29 that Russian security services commissioned the August 15 arson attack against Milrem Robotics in Tallinn. Three Latvian nationals were arrested in Latvia and transferred to Estonia. The fire was contained before causing major damage. The target is nevertheless strategically significant. Milrem produces unmanned ground vehicles and other military robotic systems and supplies equipment supporting Ukraine.
Tradecraft
The available evidence points toward the increasingly familiar Russian model:

The use of Latvian nationals is particularly consistent with Moscow’s preference for operatives who do not outwardly appear connected to Russian intelligence.
Connection to previous reporting
Milrem now joins an increasingly coherent Russian target set:
UK: drone-manufacturing facilities
Germany: defense companies and Ukrainian logistics
Romania: Ukrainian Antonov aircraft and NATO facilities
Denmark: defense companies and Ukraine-support firms
Estonia: military robotics manufacturer
This is unlikely to be coincidental target selection.
Assessed objective
The probable strategic objectives are:
disrupt Ukraine’s defense supply chain + intimidate European defense companies + demonstrate Russian reach inside NATO + impose security costs on continued Ukraine assistance.
A secondary objective may be collection of NATO response data following attribution.
Veracity
Attack occurrence: Very high.
Russian state attribution: High-moderate.
Specific Russian service: Not publicly established.
Estonia’s domestic intelligence service has formally made the attribution, and multiple independent outlets have confirmed the announcement. Russia denies responsibility.
Disinformation assessment
High likelihood of attribution-denial activity.
The Kremlin called Estonia’s accusations unfounded. That denial should be recorded but does not carry evidentiary weight comparable with an investigation involving identified suspects, arrests, and a formal counterintelligence-service attribution.
Denmark’s intelligence assessment released this week judges that a full-scale Russian invasion of NATO remains unlikely but warns that a limited Russian military attack could become possible within months. The scenarios reportedly include long-range attacks against infrastructure supporting Ukraine and potentially small-scale incursions. The Guardian
This needs careful interpretation.
The assessment does not say Russia has decided to attack NATO. Nor does NATO report unusual Russian conventional force concentrations consistent with imminent invasion. AP News
Instead, the warning concerns an increasing Russian willingness to operate across the continuum from espionage and sabotage to cyberattack, covert action, and, ultimately, limited military force.
European officials interviewed by Reuters similarly described increased sabotage, cyberattacks, drone activity, and airspace violations but said Russia currently lacks the military posture for a large conventional NATO attack. Reuters
Connection to Ratcliffe warning
This further supports the assessment from the Ratcliffe special brief. CIA Director John Ratcliffe’s August Moscow warning appears increasingly consistent with concern about a limited, ambiguous Russian operation designed to test NATO political cohesion, rather than intelligence indicating imminent armored invasion.
Assessed Russian objective
The strategic target may be NATO’s decision-making architecture more than any physical installation.
A limited attack could force allied governments to debate:
- whether Russia was responsible,
- whether the action was intentional,
- whether a proxy counts as Russian state action,
- whether Article 5 applies,
- and what proportional response is appropriate.
Creating visible disagreement would itself produce strategic effect.
Assessment: high-moderate confidence.
DOJ announced September 23 that Lee Reiber, CEO of Virginia-based Oxygen Forensics, and Russian national Oleg Sergeyevich Davydov had been arrested for allegedly concealing the company’s Russian ownership and development structure while obtaining U.S. government contracts.
DOJ criminal complaint announcement
Oxygen Forensics develops software used to recover and analyze data from electronic devices.
Affected U.S. government customers included:
- Department of Defense;
- U.S. Secret Service;
- Secret Service National Computer Forensics Institute;
- Homeland Security Investigations;
- DHS Office of Inspector General.
DOJ alleges that five Russian nationals actually owned and controlled Oxygen through a Cyprus holding company while software development remained under Davydov’s direction in Russia. The same individuals also owned Russian company MKO Systems, formerly Oxygen Software LLC, whose customers reportedly included:
- Russia’s FSB;
- Russian Investigative Committee;
- Russian Ministry of Internal Affairs.
Concealment tradecraft
After the 2022 invasion of Ukraine and subsequent sanctions, prosecutors allege the following obfuscation path:

An internal email allegedly warned that public exposure of Russian ownership could “destroy” a pending Secret Service opportunity.
Critical analytical caveat
This case is being described in some secondary reporting as a Russian attempt to “infiltrate the Secret Service.”
That currently overstates the evidence.
DOJ explicitly says: the complaint does not allege that the software contained malicious code or was used to gain unauthorized access to customer systems or data.
There is also no publicly established FSB tasking chain directing Oxygen to penetrate U.S. agencies.
Assessment
The appropriate classification is:
HIGH counterintelligence/supply-chain concern; UNPROVEN intelligence operation.
The risk is nevertheless substantial because forensic software inherently occupies a sensitive trust position.
Veracity
Concealed Russian ownership allegations: High-moderate pending trial.
Russian software development: High-moderate.
Previous Russian-security customers: High-moderate.
Malicious backdoor: No public evidence.
FSB-directed U.S. penetration: No public evidence.
This is an important case where evidentiary discipline prevents risk → suspicion → espionage attribution from becoming an unsupported chain.
Reuters reported September 23 that data allegedly stolen from the FBI by ShinyHunters contains detailed information concerning bureau personnel and assignments, including individuals working against:
- Chinese espionage,
- Russian intelligence,
- drug cartels,
- counterterrorism,
- and other sensitive missions.
The espionage significance lies less in the original criminal motivation than in the secondary intelligence value of the dataset.
Potential exploitation
Compromised personnel data can support:
identity resolution
→ organizational mapping
→ unit/function identification
→ social-media enrichment
→ family/associate mapping
→ travel identification
→ targeting or recruitment
Foreign intelligence services do not need to have conducted the original intrusion to exploit the resulting data afterward, an increasingly important distinction in modern intelligence collection. Cyber criminal acquisition is not the same as state espionage, but a criminally stolen dataset can later be acquired by a state service and repurposed for counterintelligence, targeting, recruitment, or broader intelligence exploitation.
Assessment
The dataset should therefore be treated as a potential foreign-intelligence enrichment source even absent evidence that Russia, China, Iran, or another service commissioned the original breach.
Veracity
Dataset existence: High.
Sensitive CI information contained: High-moderate based on Reuters examination.
State direction of ShinyHunters: No evidence established in this reporting.
New Zealand’s National Cyber Security Centre released its Cyber Threat Report 2026 on September 24, identifying state-linked cyber activity associated with China, Russia, Iran, and North Korea. Among these actors, the NCSC assesses the People’s Republic of China as the most persistent and capable state actor conducting cyber activity against New Zealand.
New Zealand NCSC Cyber Threat Report 2026
During the reporting year, 23% of nationally significant incidents handled by NCSC had suspected state-sponsored links. Targets included government organizations and the health, education, and IT sectors.
Chinese tradecraft
The assessment specifically highlights the PRC’s use of compromised-device networks, including home routers, to conceal operational infrastructure and support cyber operations. New Zealand associates this broader ecosystem with activity linked to Volt Typhoon, Flax Typhoon, and Salt Typhoon, with Salt Typhoon targeting spanning telecommunications, government, transportation, lodging, and military infrastructure. The strategic significance of these sectors extends beyond immediate intelligence collection, as access to them can provide persistent visibility into communications, logistics, movement, and other infrastructure that may support longer-term espionage, operational preparation, or contingency planning.
Telecommunications access can provide:
- communications collection
- credential acquisition
- network topology
- persistent access
- potential crisis-time disruption capability
Strategic objective
New Zealand assesses state cyber activity as serving national priorities including:
- diplomatic advantage,
- military advantage,
- economic interests,
- and suppression of dissent.
The country’s parallel NZSIS assessment states that China is the only country New Zealand has detected conducting espionage there “at scale.” nzsis.govt.nz
Veracity
Very high for New Zealand government’s threat assessment.
Specific incident attribution remains case-dependent.
Disinformation risk
Low for the existence of the official assessment; moderate around geopolitical interpretation.
China rejects Western allegations of state cyberespionage. The strongest evidence remains specific technical campaigns rather than nationality-based inference.
On September 22, Israel’s Haifa District Court sentenced Fares Abu al-Hija, 32, to 55 months imprisonment after he pleaded guilty to contact with a foreign agent. The Times of Israel
Abu al-Hija carried out tasks between October 2025 and January 2026, including:
- surveillance near former Defense Minister Yoav Gallant’s residence;
- recording a Tel Aviv café;
- hiding mobile phones;
- hiding money;
- concealing a cryptocurrency-wallet password.
He received approximately $3,600.
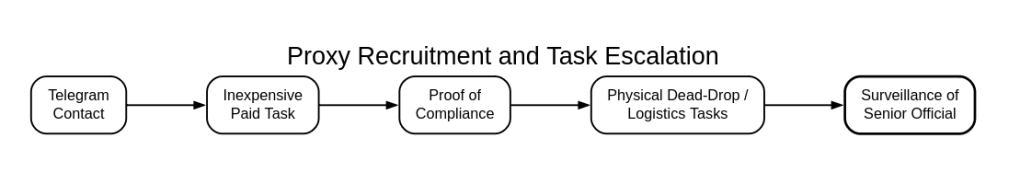
Tasking occurred through Telegram.
Tradecraft
The operation fits the established Iranian progression:

This resembles Russia’s disposable-agent architecture in one important respect:
the initial task does not need to look like espionage.
The handler can escalate assignments as the recruit demonstrates reliability.
Assessed objective
The Gallant surveillance could support:
- pattern-of-life development;
- security assessment;
- intimidation;
- assassination preparation;
- or continued intelligence collection.
There is insufficient public evidence to establish which was intended.
Veracity
Very high for contact, tasks, and conviction.
Iranian operational sponsorship: High-moderate based on prosecution evidence and the broader pattern of Iranian recruitment cases.
Azerbaijan pardoned French national Martin Ryan on September 23. He had been sentenced in March to ten years for espionage. Azerbaijani prosecutors alleged that Ryan worked for France’s DGSE collecting information on Azerbaijan’s:
- military capabilities,
- weapons,
- defense cooperation,
- foreign relationships,
- and potentially recruitable individuals.
France had rejected the accusations.
The release occurred amid a complicated diplomatic negotiation involving France, Azerbaijan, and EU sanctions against Russian-linked businessmen. Reuters reported that European diplomats viewed the detention as part of broader diplomatic bargaining. Currently
Assessment
The pardon does not establish either Ryan’s innocence or the validity of Azerbaijan’s espionage case.
It does demonstrate the continuing use of espionage prosecutions as instruments within interstate bargaining.
Veracity
Conviction and pardon: Very high.
DGSE relationship: Disputed/unresolved publicly.
Disinformation risk
High.
Both governments have strong incentives to frame the case politically. Public evidence sufficient to independently validate the alleged DGSE relationship remains limited.
Russia: defense production is becoming part of the battlespace
Milrem materially strengthens a pattern visible over several reporting cycles.
Russian collection and sabotage targets increasingly include:

This is best understood as attacking the industrial system sustaining Ukraine rather than merely attacking Ukraine itself.
The geographic boundary of the war therefore matters less to Russian intelligence than the functional boundary.
A factory in Estonia producing military robotics for Ukraine can become part of Moscow’s operational target set even though it sits deep inside NATO territory.
Assessment: high confidence.
The accumulated reporting now supports the following working model:

Milrem provides another example of the action phase.
The Danish, Romanian, British, and DOJ Russian-network cases provide evidence for the collection and recruitment phases.
The German parcel case provides evidence for the logistics reconnaissance phase.
Taken together, the evidentiary basis for a repeatable Russian sabotage methodology is substantially stronger than it was two months ago.
Confidence: high.
European reporting this week broadly converges on a common assessment: Moscow seeks to raise the political, economic, and psychological cost of supporting Ukraine while remaining below the threshold of a conventional NATO-Russia conflict. The mechanism is cumulative rather than dependent on any single spectacular attack, combining physical damage, fear, uncertainty, attribution disputes, and political division. A failed arson attempt can still signal that defense companies are reachable, a drone incursion can expose perceived vulnerabilities in NATO airspace, and a cyber intrusion can demonstrate access to critical infrastructure. In this model, the aggregate psychological and political effect may matter more than the physical consequences of any individual operation.
New Zealand’s reporting adds an important qualification to the China-Russia distinction used in previous briefs. Chinese operations remain predominantly espionage-focused, but sustained PRC access to telecommunications, transportation, government, military infrastructure, and edge devices can create latent capabilities that may be repurposed for disruption during a crisis or conflict. The resulting model is therefore best described as espionage-first access with latent disruption potential.
is more accurate than simply:
China: espionage only.
Russia, by contrast, is currently demonstrating actual physical conversion of collection into sabotage.
- Milrem operation: identify the three Latvian suspects, recruitment channel, payment method, Russian handlers, reconnaissance preceding the attack, and whether they conducted earlier assignments.
- Russian defense-industry targeting: correlate Milrem with UK drone-factory reconnaissance, German defense-company cases, Romanian Antonov surveillance, Danish defense-company reconnaissance, and Russia-nexus cyber collection against drone suppliers.
- Oxygen Forensics: determine whether Russian developers retained telemetry, update, cloud, licensing, support, or other technical access capable of exposing U.S. government forensic activity. This should be investigated without assuming a malicious backdoor exists.
- Russian proxy infrastructure: continue mapping Telegram identities, recruiters, cryptocurrency wallets, disposable accounts, and payment ranges used for surveillance and sabotage.
- FBI breach: monitor whether stolen personnel data appears in Russian, Chinese, Iranian, or criminal intelligence ecosystems.
- PRC/New Zealand: identify specific New Zealand victims associated with PRC state activity and correlate infrastructure with Salt Typhoon, Volt Typhoon, and Flax Typhoon reporting.
- Iranian recruitment: compare Abu al-Hija’s Telegram handler, payment mechanism, dead-drop methodology, and tasking language with other Israeli Iran-recruitment prosecutions.
- NATO escalation indicators: prioritize reconnaissance around defense manufacturers, Ukrainian logistics, electrical infrastructure, telecommunications, subsea cables, airports, rail systems, and military-support facilities.
The week’s strongest development is Estonia’s attribution of the Milrem Robotics arson attack to Russian security services, which moves another previously isolated-looking European incident into the category of officially attributed Russian sabotage. Milrem also fits the targeting pattern already visible across multiple independent investigations, centered on Ukraine-support logistics, drones, defense manufacturing, and critical infrastructure. Taken together, the emerging Russian model can now be described with high confidence as the operational sequence moves from an intelligence requirement through reconnaissance and the use of a disposable proxy, culminating in sabotage followed by denial.
The Oxygen Forensics case highlights a different counterintelligence vulnerability, namely trusted commercial access to national-security organizations, and warrants close scrutiny, although the available evidence does not support characterizing it as an FSB software penetration. China, by contrast, continues to operate primarily on the persistent-access side of the intelligence cycle, with New Zealand publicly identifying the PRC as its most persistent and capable state cyber actor, while acknowledging that such access can create latent disruptive potential during a future crisis. Iran’s Abu al-Hija case reinforces another recurring pattern, demonstrating how foreign intelligence services can use Telegram contact, modest payments, and incremental tasking to convert remote recruitment into physical surveillance and clandestine logistics inside an adversary state.
Current assessments
- Russian espionage-to-sabotage campaign against NATO/European Ukraine-support infrastructure: HIGH confidence, increasing.
- Russian defense-industrial targeting, particularly unmanned systems: HIGH confidence.
- Near-term limited Russian provocation against NATO: Elevated but uncertain; no public evidence of an attack order.
- Oxygen Forensics as a counterintelligence/supply-chain exposure: HIGH concern.
- Oxygen Forensics as a proven Russian intelligence penetration: NOT ESTABLISHED.
- PRC cyber-espionage against New Zealand and Five Eyes interests: HIGH confidence.
- Iranian remote recruitment of local proxies for surveillance and logistics: HIGH confidence.
The indicator I would prioritize most heavily for the next cycle is cross-domain convergence around the same physical target. When a defense company is being researched online, photographed by locally recruited individuals, probed electronically, and discussed by proxy actors at roughly the same time, that combination should be treated as potential pre-operational intelligence preparation, rather than four unrelated security events.
如有侵权请联系:admin#unsafe.sh