Reporting period: 22–29 September 2026Scope: State and state-aligned cyber espionage, CNE, intel 2026-9-29 16:56:39 Author: krypt3ia.wordpress.com(查看原文) 阅读量:4 收藏
Reporting period: 22–29 September 2026
Scope: State and state-aligned cyber espionage, CNE, intelligence collection, access operations, supply-chain exposure, and espionage-enabling tradecraft.
Executive assessment
The week’s cyber-espionage reporting reinforces a broader trend we have been tracking: state cyber operations are increasingly about acquiring durable access rather than simply stealing a discrete collection of documents.
The most significant development is the continued exposure of a shared Chinese zero-day exploitation ecosystem. Volexity identified another China-aligned cluster, UTA0565, using the same chained Chrome and Windows vulnerabilities previously observed across several other PRC-aligned espionage actors. The individual operators retained distinct targeting, infrastructure, and payloads, but shared essentially the same underlying exploitation capability. Volexity assesses that this pattern suggests coordination within the Chinese CNE community, with a core exploitation framework likely being distributed, customized, and operationalized by multiple groups. Volexity
That development is reinforced strategically by New Zealand’s 2026 Cyber Threat Report. New Zealand’s NCSC describes the PRC as its most persistent and capable state cyber actor, while reporting 86 of 369 nationally significant incidents during the reporting year as having suspected state-sponsored links. The agency specifically warns that cyber espionage accesses may remain dormant for months or years before being used for intelligence collection or potentially disruption. NCSC NZ
Russia presents a different problem this week. The Oxygen Forensics case exposes a potentially serious trusted-technology and counterintelligence vulnerability, but the evidence needs to be bounded carefully. DOJ alleges Russian nationals secretly owned and controlled a company providing digital-forensics technology to sensitive U.S. government organizations while the technology itself was developed in Russia. However, DOJ explicitly states that its complaint does not allege malicious code or unauthorized access to customer systems or data. Justice Department
North Korea continues expanding the overlap between human infiltration, cyber access, intelligence collection, and revenue generation, while Iranian operations remain heavily oriented toward surveillance of individuals and credential/device compromise.
My overall assessment for the week is therefore:

That progression is becoming more important than malware family attribution alone.
Assessment: HIGH confidence
Volexity disclosed that UTA0565 exploited three vulnerabilities against Chrome/Chromium and Windows on September 3–4, while the vulnerabilities remained effectively un-patched:

UTA0565 used phishing and cloned websites impersonating legitimate organizations, including media organizations and NGOs. Asian government organizations were among the observed targets. Volexity
The operation ultimately deployed a previously undocumented implant Volexity calls CLEANGULP.
The malware provides:

CLEANGULP established persistence using a scheduled task named MicrosoftIME, installed itself beneath %LOCALAPPDATA%\Microsoft\IME\, and communicated with attacker infrastructure through encrypted HTTP.
But CLEANGULP is not the most significant intelligence finding. The exploit distribution model is.
Proofpoint previously observed APT31/TA412, UNK_LateNight, UNK_DoubleCheck, and UNK_QuietRacket using the same BlueMoon exploitation chain. Targets included U.S. NGOs, aerospace organizations, mining and commodity companies, and government, financial, consulting, and manufacturing organizations in Southeast Asia. CyberScoop
Recorded Future News reports Proofpoint researchers found the underlying exploit code sufficiently similar to conclude the groups were using the same kit rather than independently developing equivalent exploits. The Record from Recorded Future
Intelligence significance
This increasingly resembles a capability distribution architecture in which vulnerability discovery or reverse engineering feeds centralized exploit development, which is then converted into a weaponized exploit framework and distributed across multiple PRC-aligned operators. Those operators can subsequently pair the shared exploit capability with their own infrastructure, lures, and malware before conducting intelligence collection. The structure is particularly significant when considered alongside the Integrity Technology material previously analyzed, because it suggests a broader ecosystem in which centrally developed technical capabilities can be operationalized by distinct actors while preserving operator-specific tooling, infrastructure, and targeting patterns.
The Chinese cyber ecosystem increasingly appears capable of separating capability development from operational execution. Contractors, vulnerability researchers, platform developers, intelligence units, and operational teams do not necessarily need to reside inside the same organization. This would allow expensive capabilities such as zero-days to be industrialized and reused across otherwise compartmented operations.
Assessment: HIGH confidence
New Zealand’s NCSC released its Cyber Threat Report 2026 on September 24.
The report identifies China, Russia, Iran, and North Korea as sources of suspected state-sponsored cyber activity but describes the PRC as the most persistent and capable state actor conducting cyber activity against New Zealand. NCSC NZ
New Zealand reported:
369 nationally significant incidents
of which
86 had suspected state-sponsored links.
Targets included government, health, education, IT managed-service providers, and organizations holding information capable of providing strategic advantage. Reuters
The NCSC also reiterates previous warnings concerning Salt Typhoon, Volt Typhoon, and Flax Typhoon. Its report notes Salt Typhoon activity targeting telecommunications, transportation, and government networks for collection including credentials, calls, network information, and other data. NCSC NZ
Intelligence assessment
This supports the distinction developed in the parallel espionage reporting: Russian intelligence access is increasingly associated with sabotage preparation and coercive operations, while Chinese access is generally optimized for persistent strategic collection while also creating potential contingency access for future crises or conflict. The categories are not mutually exclusive. A compromised telecommunications provider, for example, can support SIGINT collection in the present while simultaneously providing network mapping, credential access, communications visibility, and a latent capability for disruption later. The key implication is that espionage access should not be treated as purely an espionage capability, because persistent access is itself a strategic asset that can be repurposed as operational requirements change.
Assessment: HIGH confidence regarding ownership allegations; LOW confidence for any Russian intelligence exploitation of U.S. systems
The U.S. Justice Department alleges that Oxygen Forensics represented itself as an independent U.S. company while five Russian nationals actually owned and controlled the company through a Cyprus holding structure. DOJ also alleges that software represented as American-developed was developed in Russia. Justice Department
Customers reportedly included components of:
- Department of Defense
- Department of Homeland Security
- Secret Service
- Homeland Security Investigations
- National Computer Forensics Institute
The Russian-associated company reportedly sold related software to organizations including the FSB, Russian Investigative Committee, and Russian Ministry of Internal Affairs. The Record from Recorded Future
This creates an obvious CI question because digital-forensics platforms can interact with extraordinarily sensitive investigative material.
However, this distinction is critical:
DOJ does not allege that Oxygen software contained malicious code or was used to obtain unauthorized access to U.S. customer systems or data. Justice Department
Current evidence supports an assessment of Russian ownership or control concealment, Russian development activity, and deployment within sensitive U.S. government environments as a serious supply-chain and counterintelligence exposure, but it does not presently support the more specific claim that the FSB penetrated U.S. agencies through Oxygen software. Those are materially different judgments. The relevant intelligence requirement therefore extends beyond determining whether the software contained a backdoor and should include whether Russian-controlled personnel could obtain visibility through development environments, licensing infrastructure, telemetry, and update mechanisms. The case fits a broader intelligence chain of a trusted vendor serving a sensitive customer can gain privileged technological access that creates operational visibility and, in turn, a potential intelligence opportunity demonstrating that meaningful intelligence access can exist even in the absence of malware or a deliberately implanted backdoor.
Assessment: HIGH confidence
New Zealand’s report also documents a North Korean IT worker obtaining employment with a large New Zealand business through a false persona. According to reporting based on the NCSC case, the individual used fake identity documents, a New Zealand contact address, and recruited a New Zealand citizen to receive and operate the employer’s laptop. When discovered and terminated, the worker claimed to possess commercially sensitive information and threatened disclosure unless paid. The Standard
This aligns closely with the DPRK laptop-farm ecosystem we previously examined.
The model is:

This is fundamentally different from a traditional intrusion because there may be no exploit, phishing email, or initial malware deployment; instead, the attacker simply becomes an authorized user.
The FBI’s September alert on North Korean WaterPlum/Contagious Interview activity further demonstrates the convergence between fake employment activity and malware delivery targeting IT professionals. Internet Crime Complaint Center
The DPRK model increasingly combines:

This makes DPRK operations particularly difficult to classify cleanly as either cybercrime or espionage.
Assessment: MODERATE-HIGH confidence
Iranian activity remains differentiated from the PRC and Russian models by its continued emphasis on individual targets, particularly dissidents, activists, journalists, and politically relevant persons. Recent reporting continues tracking Iranian-linked deployment of CHOSEN BRICK/HEAVYGRAM against those communities, with capabilities including collection of messages, contacts, email, screenshots, and microphone data. AcidPeak
The FBI’s September advisories likewise highlighted Iranian cyber targeting of dissidents, activists, and journalists and the use of Telegram C2 infrastructure to deliver malware to identified targets. Internet Crime Complaint Center This is important because the Iranian intelligence objective frequently extends beyond conventional information theft.
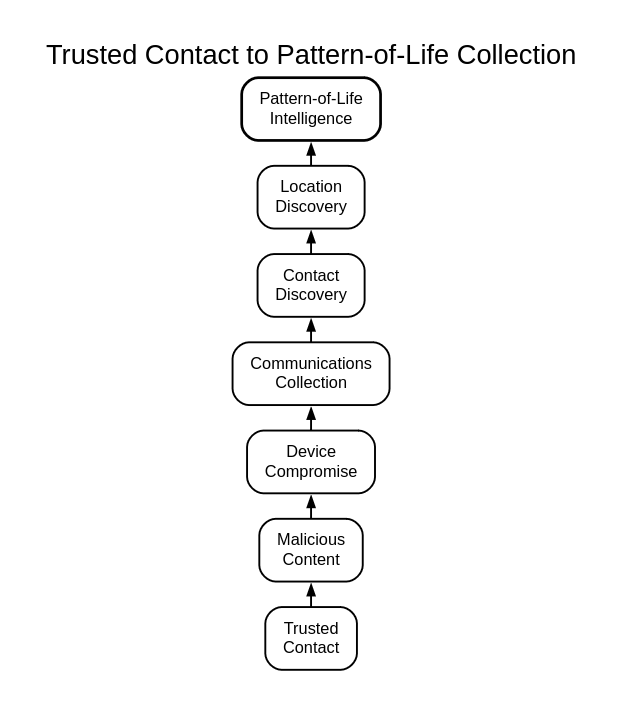
The collection chain can become:

This access can subsequently support surveillance, coercion, targeting, and physical operations, reinforcing the human-cyber convergence identified in previous reporting.
Assessment: MODERATE confidence on espionage motivation; LOW confidence on sponsor
A separate development worth watching is NightEagle/APT-Q-95. Kaspersky reportedly identified the group expanding into Russian corporate targets after previously being associated with attacks against strategically important Chinese organizations. The earlier Chinese targeting reportedly included defense, semiconductor, AI, and quantum-technology organizations. The Record from Recorded Future
Observed tradecraft against Russian organizations included:

Kaspersky did not publicly identify the Russian victims or attribute the activity to a state. Chinese researchers have previously suggested a North American connection, but that attribution has not been independently substantiated.
NightEagle is best assessed as a probable espionage-motivated actor with unresolved state sponsorship and supported geographic expansion, while its targeting profile is particularly notable for its concentration on strategic technology acquisition rather than generalized government intelligence collection.
Across the week’s reporting, several seemingly unrelated operations converge around a common principle:
| Actor/ecosystem | Initial access | Primary intelligence target | Strategic value |
|---|---|---|---|
| PRC/UTA0565 | Zero-day chain | Governments | Political/strategic intelligence |
| PRC/Salt Typhoon ecosystem | Edge/network infrastructure | Telecom/network data | Persistent SIGINT-like access |
| Russia/Oxygen exposure | Trusted commercial technology | Sensitive government customers | Potential CI/supply-chain visibility |
| DPRK | Synthetic employee identity | Corporate systems/data | Revenue + access + intelligence |
| Iran | Social engineering/device compromise | Individuals | Communications/POL intelligence |
| NightEagle | Stolen VPN credentials | Strategic technology organizations | Technology/intellectual property |
The technical implementations differ, but the strategic objective remains remarkably consistent: gain access to something the target already trusts. That trusted object may be a browser, network appliance, software vendor, employee, Telegram contact, or VPN credential. Once that trust boundary is crossed, the espionage problem shifts from gaining initial access to maintaining persistence, preserving access, and collecting useful intelligence over time.
The week’s strongest cyber-espionage development is the growing evidence that China possesses an ecosystem capable of distributing sophisticated exploitation capability across multiple operational clusters.
- UTA0565 matters less as another new APT name than as evidence of how the Chinese CNE apparatus may operationalize vulnerabilities. The same underlying exploitation capability appeared across multiple independently operating espionage groups while the vulnerabilities were still operationally valuable. Volexity
- The Oxygen Forensics case exposes the complementary problem: an intelligence service does not necessarily need to hack its way into a target when foreign-controlled technology already occupies a trusted position inside the target environment. Current evidence does not demonstrate Russian exploitation of that access, but the exposure warrants CI investigation. Justice Department
- DPRK operations demonstrate the same principle at the human layer: rather than compromise the employee, become the employee.
- Iran demonstrates it at the personal layer: compromise the trusted communication channel or device and turn digital access into intelligence about the human target.
Taken together, the emerging cyber-espionage model begins with an intelligence requirement, followed by identification of a trusted access path, acquisition of that access, establishment of persistence, intelligence collection, expansion of access, and retention of the capability for future intelligence or operational use. This is the cyber counterpart to the Russian physical-espionage model, in which an intelligence requirement drives reconnaissance, use of a disposable proxy, sabotage, and subsequent denial.
如有侵权请联系:admin#unsafe.sh