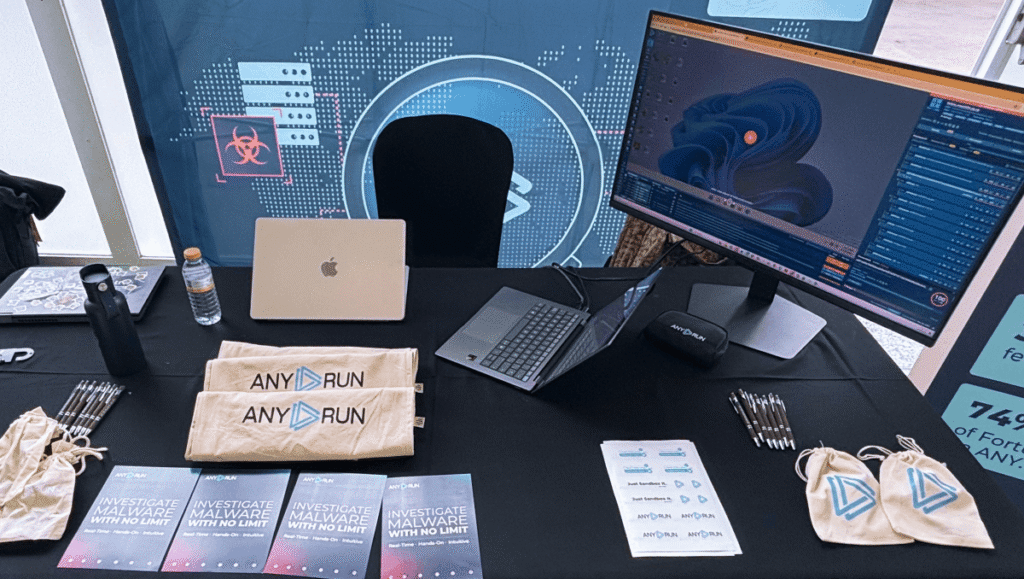
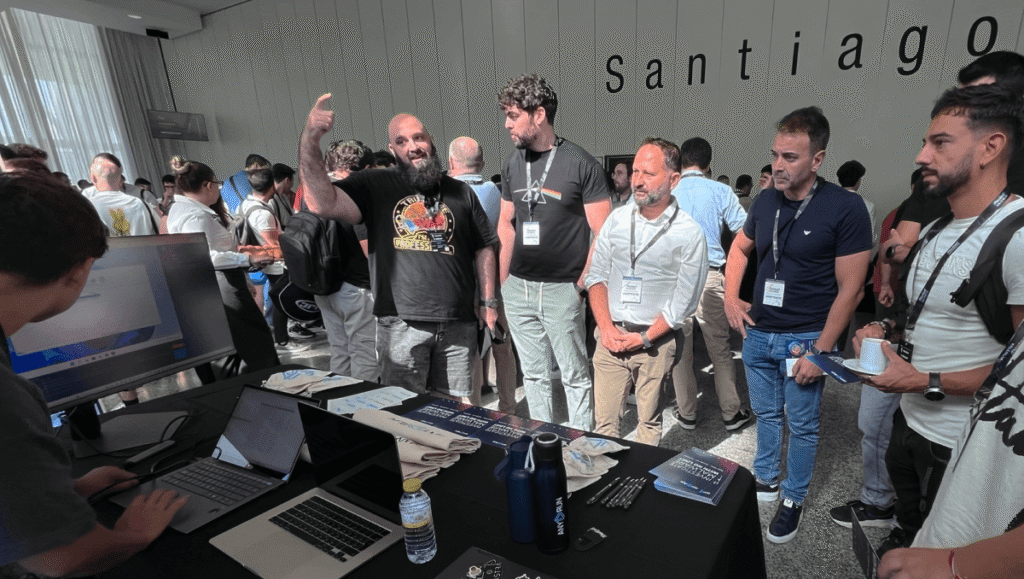
ANY.RUN once again joined the RootedCON community this year, taking part in Rooted Valencia 2026 on September 18. The event brought together cybersecurity professionals, researchers, hackers, and technology enthusiasts from across the global cybersecurity community.
For our team, the event became yet another opportunity to meet security professionals, speak with clients, and demonstrate how interactive sandboxing and threat intelligence can support SOCs and MSSPs at any scale. We also shared some of the latest capabilities designed to help analysts investigate incidents faster and get more context from their findings.
Rooted Valencia Agenda 2026
The Valencia edition of RootedCON covered a wide range of topics, from AI agents and prompt injection to cloud security, command-and-control, and malware research.
Several sessions explored how emerging technologies are changing the attack surface, while others focused on established techniques used in modern attacks. AI was particularly prominent, with discussions around rogue agents, small language models, and authentication for AI agents.
Connecting with Security Teams
RootedCON gave us the chance to learn more about how security teams are integrating ANY.RUN into their existing workflows. We learned more about how our users apply interactive sandboxing during investigations and implement threat intelligence to connect findings, uncover related activity, and add context to their cases.
These conversations offered valuable insight into the different ways SOCs and MSSPs work with our solutions and the challenges they encounter in their day-to-day operations.
Taking a Closer Look at ANY.RUN’s Capabilities
At the ANY.RUN booth, we demonstrated how interactive analysis can help security teams move beyond an initial alert and understand what a suspicious object actually does.
With the Interactive Sandbox, analysts can execute files and URLs in controlled environments, observe their behavior in real time, and examine processes, network connections, files, commands, and other activity generated during execution. This visibility helps triage alerts faster, improve detection accuracy, reduce unnecessary escalations, and respond to confirmed threats more quickly.
Phishing alerts are another common use case for this approach. Suspicious links and attachments can be analyzed in a controlled environment to reveal redirects, downloaded payloads, network connections, and other activity that may not be apparent from the original message alone. This can give analysts more context when assessing potentially malicious emails and deciding how to respond.
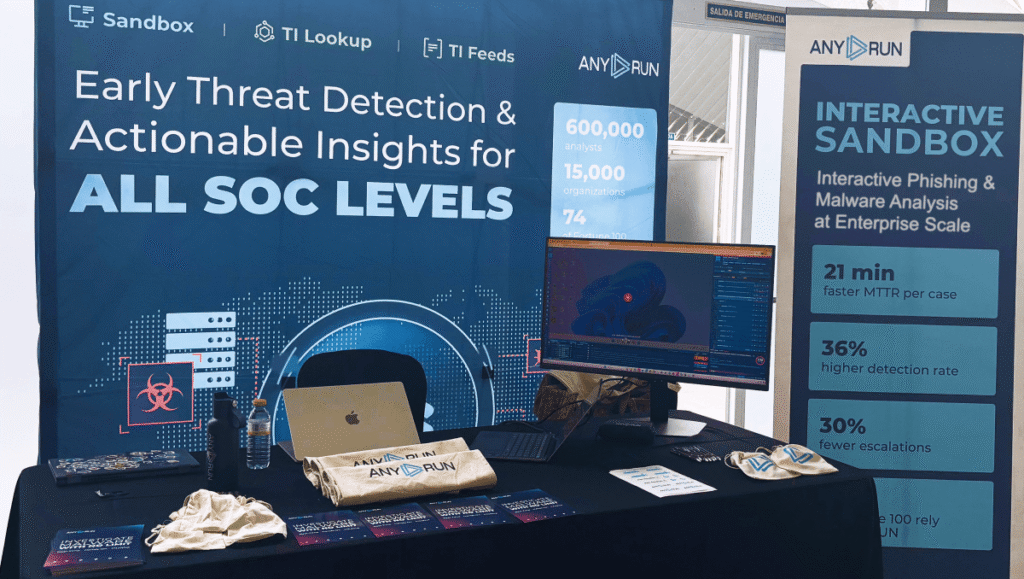
The information uncovered during analysis can also become the starting point for a wider investigation. Indicators discovered during a session can be used to search for related samples, domains, IP addresses, and other artifacts through ANY.RUN’s threat intelligence capabilities. This allows analysts to speed up investigations, uncover connections between related threats, and reduce the manual work involved in tracing attack infrastructure.
For security teams, combining behavioral analysis with threat intelligence can help connect individual phishing alerts to the broader activity behind them, rather than treating each case as an isolated event.
What We Heard from Security Teams at RootedCON Valencia
Many of our conversations at RootedCON Valencia 2026 came back to a familiar challenge: security teams need to investigate more activity without adding unnecessary manual work.
Whether the case involves a phishing attachment, suspicious URL, or unfamiliar malware sample, analysts need enough context to understand what happened and decide what to investigate next.
That is the role interactive threat analysis can play for SOCs and MSSPs. By giving analysts direct visibility into execution and the indicators it produces, ANY.RUN helps turn individual alerts into investigations with more context.
From Rooted Valencia to the Next Investigation
Rooted Valencia brought together a wide range of perspectives on cybersecurity, from emerging AI-related risks to established techniques used in malware and intrusion campaigns.
The combination of execution visibility, behavioral analysis, and threat intelligence gives analysts more than a simple malicious-or-benign verdict. It provides evidence they can examine, indicators they can investigate, and context they can use to understand a threat.
Thank you to everyone who visited the ANY.RUN booth, shared their experiences, and spoke with our team in Valencia.
We look forward to continuing the conversation at the next event.
About ANY.RUN
ANY.RUN provides interactive malware analysis and threat intelligence to more than 16,000 organizations and 700,000 security professionals worldwide.
The solutions include the Interactive Sandbox, Threat Intelligence Lookup, and Threat Intelligence Feeds, helping SOC and MSSP teams investigate suspicious files and URLs, uncover connections between threats, and gain more context during security investigations.
ANY.RUN also maintains a strong focus on security and data protection. The company is SOC 2 Type II certified, reflecting its commitment to robust security controls and the protection of customer information.