Reporting period: September 7–14, 2026Scope: State and state-aligned cyber operations, APT activ 2026-9-14 15:31:5 Author: krypt3ia.wordpress.com(查看原文) 阅读量:8 收藏
Reporting period: September 7–14, 2026
Scope: State and state-aligned cyber operations, APT activity, technical campaign intelligence, active exploitation, and cyber-enabled military/intelligence activity.
Executive assessment
Three developments dominate this reporting period.
First, a common exploit-supply mechanism has become visible across multiple Chinese and China-aligned espionage clusters. Proofpoint and Volexity independently documented BlueMoon, a shared exploit chain combining two Chromium/V8 vulnerabilities with a Windows kernel privilege-escalation flaw. Four espionage-oriented clusters adopted the same core exploitation capability within days, while using separate infrastructure and post-exploitation payloads. This is strong evidence of either centralized capability distribution, a common exploit broker/developer, or rapid capability sharing within the PRC offensive ecosystem. (Proofpoint)
Second, Russian state-linked cyber operations have crossed an important AI threshold. Anthropic identified GTG-20006, whose targeting and tradecraft it says are consistent with Midnight Blizzard, using AI not simply for coding assistance but as an operational layer spanning infrastructure acquisition, phishing, malware modification, C2 management, credential collection, and exfiltration. AI agents automatically rebuilt malware when detection occurred. (Anthropic)
Third, the broader state threat landscape is converging on agentic exploitation. Google’s September 8 threat report separately observed PRC espionage actors building automated exploitation pipelines, Sandworm using Gemini to support phishing, password spraying, host fingerprinting, and infrastructure concealment, APT42 using generative AI throughout targeting and collection, and DPRK clusters integrating AI into social engineering, backdoor development, lateral movement, and source-code/repository poisoning. (Google Cloud)
The week’s most important intelligence judgment is therefore broader than any single malware family:
AI is moving from an adversary productivity aid into an orchestration layer for intelligence operations.
This does not eliminate traditional tradecraft. It makes reconnaissance, exploit development, credential operations, infrastructure management, malware adaptation, and collection faster and cheaper.
Priority: Critical
Primary actors: TA412/JungleBamboo/Violet Typhoon/APT31, UTA0560, UNK_LateNight, UNK_DoubleCheck, UNK_QuietRacket
Primary nexus: PRC for several clusters
Attribution confidence: High for TA412/JungleBamboo; variable for other clusters.
Proofpoint disclosed BlueMoon on September 9 after observing four espionage-focused clusters using essentially the same exploit chain. Volexity independently observed two Chinese actors using byte-for-byte identical shellcode but different post-exploitation malware and infrastructure. (Proofpoint)
The exploit chain combines:
- CVE-2026-85046, Chromium V8 type confusion.
- CVE-2026-87491, V8 sandbox escape.
- CVE-2026-85880, Windows kernel privilege escalation involving ALPC/WNF functionality.
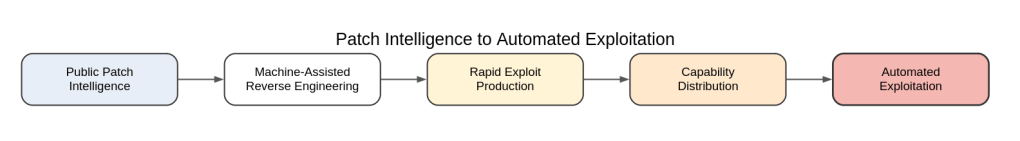
The operational significance lies in the patch gap. CVE-2026-85046 was fixed in upstream Chromium source on August 7, but the fix did not reach stable Chrome until September 3. Attackers therefore had weeks in which the patch was public enough to reverse engineer while end users still lacked an available stable update.
Exploit sequence
BlueMoon first obtains arbitrary V8 memory read/write, then corrupts WebAssembly metadata to escape the V8 sandbox. A reflectively loaded DLL fingerprints the Windows build and token state. If appropriate, the Windows kernel exploit enables SeDebugPrivilege, after which shellcode injects into the Chrome broker process and executes an operator-specified command outside the sandbox.
The default execution chain is conspicuously simple:
curl → %TEMP%\msgbox.exe → execute
That simplicity is analytically important. Proofpoint assesses that the developers prioritized speed of deployment over OPSEC, consistent with exploitation of a narrow patch window.
Supported Windows builds observed
- 17763
- 19041–19045
- 20348
- 22000
These map principally to older Windows 10, Server 2019/2022, and early Windows 11 releases.
TA412 / JungleBamboo / APT31
TA412 began deploying BlueMoon on August 28 against a small number of U.S. NGOs, mining organizations, and physical commodity traders. Proofpoint connects TA412 to the PRC MSS Hubei State Security Department and Wuhan Xiaoruizhi Science & Technology through prior U.S. government attribution.
Initial access relied on targeted spearphishing, including:
- University internship requests.
- Academic conference themes.
- Target-specific rapport building.
Successful exploitation installed a malicious Chromium extension called GemStone, masquerading as a Google Gemini browsing assistant.
GemStone capabilities include:
- Keylogging.
- Cookie theft.
localStorageandsessionStoragetheft.- Browser-session metadata collection.
- Screenshot capture.
- Keyword-triggered surveillance.
- Arbitrary HTTP requests.
- Command polling and remote tasking.
This is a particularly effective espionage payload because authenticated browser sessions increasingly provide direct access to SaaS, webmail, collaboration platforms, and cloud consoles without requiring traditional credential replay.
UNK_LateNight
Beginning September 2, UNK_LateNight targeted U.S. aerospace companies, using B2B and request-for-quotation lures tied to the U.S. defense-industrial base.
The BlueMoon chain ultimately delivered ShadowPad through DLL sideloading. Persistence used:
EdgeCore_AutoUpdate
The associated ShadowPad deployment stole Firefox profile data, sniffed traffic, and communicated over HTTPS to:
ms.checrity[.]com
Proofpoint assesses this cluster as China-aligned.
UTA0560
Volexity observed UTA0560 targeting NGOs using financial/donation-themed phishing.
A reflected XSS flaw on a legitimate U.S. university website redirected victims to:
cloud.shinewrist[.]net
The final implant was GRIMWEDGE, a JScript backdoor capable of:
- Host reconnaissance.
- Directory listing.
- File reading.
- File deletion.
- Process enumeration.
- Process termination.
- Command execution.
- Payload upload. (Volexity)
Persistence used a scheduled task:
Windows Scheduled System
and a victim-specific C2 staging mechanism tied to %COMPUTERNAME%.
Why multiple actors matter
Volexity found that JungleBamboo and UTA0560 used:
- Identical exploit shellcode.
- Separate infrastructure.
- Different payload families.
- Different compilation environments.
- Different operational histories.
Volexity therefore assesses with low confidence that the exploit chain may have been sold or provided to separate Chinese operators, rather than independently developed by each actor.
Assessment
This resembles a capability-distribution ecosystem more than spontaneous tool reuse.
Possible models include:
- MSS or PLA central capability development.
- A shared Chinese contractor.
- A commercial offensive-security supplier.
- Direct sharing between affiliated operators.
Current evidence does not distinguish conclusively among them.
Capability-sharing assessment: High confidence.
Central government distribution: Moderate confidence.
Commercial exploit-broker model: Plausible but unproven.
Priority: Critical
Actor: GTG-20006
Assessed overlap: Midnight Blizzard / APT29
Attribution confidence: Moderate to High.
Anthropic’s September threat report provides one of the clearest documented cases yet of a state-nexus espionage actor operationalizing AI across almost the entire intrusion lifecycle.
Anthropic states its attribution is consistent with public reporting on Midnight Blizzard. One operator used the Russian-language handle:
JackPoterz (Anthropic)
Targets included:
- Ukrainian government personnel.
- Ukrainian military organizations.
- Diplomatic staff.
- European governments.
- Intelligence organizations.
- Defense organizations.
- Think tanks.
- U.S.-foreign-policy-linked individuals.
- Drone manufacturers and supply-chain firms.
- Asian maritime-government organizations.
Anthropic identified more than 20 distinct organizations involved in targeting, reconnaissance, or live operations.
AI-enabled workflow
GTG-20006 used AI-assisted systems for:
- Malware development.
- Infrastructure acquisition.
- Domain registration.
- Phishing.
- Malware deployment.
- Persistence.
- C2 monitoring.
- Credential theft.
- Exfiltration.
- Malware detection testing.
- Automated malware rebuilding.
The malware ecosystem included:
- Two Windows implant families.
- A mobile exploitation kit.
- Browser password-store credential theft.
- A phishing platform.
- An administrative console managing compromised accounts.
Autonomous AV/EDR adaptation
The most consequential feature was an automated malware-evasion loop.
AI agents monitored whether deployed tooling was detected by security products. If detection occurred, the system autonomously:
- Modified the code.
- Rebuilt the malware.
- Retested it.
- Repeated the loop until detections stopped.
- Restaged the resulting malware for operations.
This compresses what historically required an operator/developer feedback cycle into an automated process.
Initial-access methods
Documented methods included:
- Spearphishing.
- ClickFix.
- DNS hijacking.
- Compromised Wi-Fi providers.
- Credential theft.
- Mobile-device compromise.
Hospitality infrastructure compromise
The actor compromised at least three hotel guest-Wi-Fi providers.
Using stolen administrative credentials, operators modified DNS records to redirect guests to actor-controlled infrastructure. Victim traffic, device identifiers, and IP addresses were collected, after which ClickFix-style pages delivered Windows, Android, or iOS malware.
Individuals associated with Ukraine and drone technology were specifically prioritized.
This overlaps with Microsoft’s previously reported CaptiveCrunch tradecraft.
Drone-industrial targeting
GTG-20006 bulk-exfiltrated mailboxes from at least two drone-component manufacturers and stole the complete proprietary SDK for a drone vision system.
The actor subsequently reverse-engineered:
- Product architecture.
- Hardware BOM.
- Supplier dependencies.
- AI/vision firmware.
- Details of an unreleased product.
Assessment
This appears to be direct battlefield-industrial intelligence collection.
The targeting suggests Russian intelligence requirements around:
- Ukrainian UAV capability development.
- Supply-chain chokepoints.
- Vision and guidance technologies.
- Component dependencies.
- Future product capabilities.
Strategic objective confidence: High.
Google Threat Intelligence separately reported that SANDWORM RELIC, its designation covering activity previously associated with Sandworm/APT44/FROZENBARENTS, has integrated Gemini into operations targeting Ukraine. (Google Cloud)
Observed use included:
Initial access
- AI-themed phishing domains.
- Automated asynchronous password-spraying scripts.
Internal reconnaissance
- Endpoint fingerprinting.
- Automated host profiling.
Infrastructure concealment
- Proxy-routing automation.
- C2 backend hiding.
- Locally built projects interfacing with Gemini APIs.
No new destructive payload was publicly disclosed in this reporting.
The significance is tradecraft evolution: Sandworm is experimenting with automation around high-volume credential and reconnaissance tasks, rather than replacing its core offensive tooling.
Attribution confidence: High for GTIG’s actor tracking.
Operational impact disclosed: Moderate.
Anthropic also disclosed GTG-10007, a Chinese-speaking cluster believed to be operating from Changsha, Hunan Province.
At least two operators were reportedly university students studying computer and communications engineering. One had previously interned at Sangfor and was interviewing for an offensive cyber role at QiAnXin.
Anthropic observed parallel workstreams for:
- Foreign-government reconnaissance.
- Live exploitation.
- Malware development.
- Vulnerability research.
- Intelligence collection.
- Exploit development against security appliances.
- Post-exploitation.
The group targeted roughly 50 organizations, spanning:
- Government.
- Education.
- Energy.
- Technology.
- Healthcare.
- Finance.
- Manufacturing.
Confirmed compromises reportedly included an education-technology provider, a commercial production environment, and a Southeast Asian government agency whose citizen records were accessed.
Autonomous exploit development
GTG-10007 maintained what Anthropic describes as an AI-driven exploit foundry.
Its workflow:
firmware → unpack → decompile → identify candidate flaw → generate exploit → lab-test → modify → retest → retain successful exploit
The system used parallel agents and persistent campaign memory.
One network-appliance workstream reportedly generated more than a dozen possible zero-day findings in one month.
Anthropic further observed exploitation attempts against the same class of appliances at government organizations.
Attribution caution
This is strong evidence of Chinese-origin offensive activity.
It is not public proof that GTG-10007 was directly controlled by MSS or PLA.
The operators’ education, security-company ties, target selection, and intelligence priorities make a future or current state/contractor relationship plausible, but that remains analytic inference.
Chinese origin: High confidence.
Espionage intent: High.
Direct PRC government tasking: Moderate/Unconfirmed.
Google’s September report independently documented continuing AI use by established PRC espionage actors.
BASIN CASTLE
BASIN CASTLE, formerly tracked by Google as BASIN/TEMP.Hex, used AI across:
- High-value target profiling.
- Localization of spearphishing lures.
- Malware development.
- API-resolution obfuscation.
- Rolling-XOR protection of C2 IPs.
- PowerShell troubleshooting.
- Active Directory reconnaissance.
RAVINE CASTLE / APT24
RAVINE CASTLE, previously tracked as COULEE/APT24, used Gemini to research:
- Foreign ministries.
- International organizations.
- VMware vCenter SAML bypasses.
- Active Directory exploitation.
- Rubeus/Kerberos techniques.
- Credential-harvesting methods.
Google also observed this actor using AI to assist with processing exfiltrated intelligence into structured products and investigating how data could be anonymously leaked to media and social-media influencers.
Assessment
This is particularly relevant to intelligence doctrine.
AI is now being used on both sides of the collection cycle:
before compromise: targeting and access development;
after compromise: exploitation, processing, translation, summarization, and dissemination.
Google documented continued AI use by CALANQUE ION, which it maps to Iranian government-backed APT42.
Observed uses included:
- Identifying specific individuals.
- Discovering target email addresses.
- OSINT enrichment.
- Local-language lure generation.
- Staging-infrastructure development.
- Reverse engineering.
- Research aimed at bypassing software licensing and EDR controls.
- Summarizing exfiltrated information. (Google Cloud)
This is consistent with APT42’s longstanding emphasis on individualized social engineering and credential operations.
The notable change is not a new initial-access technique. It is scale and target-preparation efficiency.
Attribution: High confidence.
Anthropic disclosed additional Iran-nexus operations that materially expand the current intelligence picture.
GTG-30004
An Iranian-linked actor used Claude to construct an automated identity-profiling harness targeting:
- Israeli government individuals.
- Israeli nongovernmental individuals.
- U.S. individuals.
- Jewish diaspora organizations.
The same actor modified NanoDump, an open-source LSASS credential dumper, and built a custom C++ obfuscation pipeline to rename identifiers and inject dummy functions.
This activity combines classic targeting intelligence with endpoint credential-access tooling.
GTG-30005
A separate Iran-nexus actor used Claude to develop targeting-oriented intelligence on U.S. naval forces.
Collection included:
- Ship and aircraft transponder identifiers.
- Military personnel derived from photo captions.
- Commercial satellite-imagery workflows.
- Public websites exposing naval movement.
- Known vulnerabilities affecting shipboard technologies.
- Maritime VSAT terminals.
- Cisco communications systems.
- Industrial-control products. (Anthropic)
Assessment
This is not proof of imminent attack preparation.
However, the collection is more operationally relevant than generic OSINT because it combines:
location + personnel + systems + vulnerabilities.
That is the structure of a targeting package.
Iran nexus: High confidence from platform telemetry.
Specific agency attribution: Not publicly established.
Google’s MIDNIGHT NEPTUNE, formerly UNC1069, represents DPRK-linked financially motivated and espionage-adjacent clusters targeting cryptocurrency organizations.
Google observed:
- AI-generated social-engineering personas.
- Technical troubleshooting lures.
- Python RAT development.
- Cross-platform persistence.
- Process injection.
- Fileless execution.
- Bash scripting for lateral movement.
- Poisoned internal repository configurations.
- Manipulation of Claude CLI hooks.
- Deployment of a backdoor called SOMBERMEME upon developer interaction. (Google Cloud)
This activity fits North Korea’s increasingly blurred model of:
revenue collection + espionage + software-supply-chain access.
Developer environments remain especially attractive because they can expose source code, CI/CD secrets, signing systems, cloud credentials, and downstream customers.
BlueMoon / UTA0560
Domains
cloud.shinewrist[.]net
ocr.opusaccel[.]top
Infrastructure
206.166.251[.]164
Hashes
Files1.htmld17053557bb90298f7b115432b4820a248fdbe678bca31721529b1f51a82343b
react.min.js337b48c1cd6dd6e7b8073327082a60e149517fa084ba17b180e041fffa3b130d
page.html7a52ff23949edee8faa61ce0def6dbca8b7e5943c54d23376cc190762ea3985c
p1 datacd0c21f9b32b7feeda1787fccab622dec60ecdf84c0538c08bde3946856b0fa0
p1 DLLb7b0cd6539464ab39c6526e499f86d611faa21c5af945535ebaf187cec543af1 (Volexity)
JungleBamboo / APT31
photos.msbenefit[.]com
proof.gitprogram[.]com
xyz0102.gitprogram[.]com
Malicious extension ID:
ckiknalbeplpcpofpnabcnhjcegckfei (Volexity)
UNK_LateNight
ms.checrity[.]com
Persistence:
EdgeCore_AutoUpdate
File:
A08744D2.tmp (Proofpoint)
Russian/Midnight Blizzard-aligned activity
Anthropic published historical attacker egress addresses associated with activity in its cyber investigation, including:
162.128.129[.]106
195.178.110[.]131
45.148.10[.]242
92.118.39[.]3
185.65.134[.]246
185.65.134[.]199
193.32.249[.]161
193.32.249[.]164
193.32.249[.]170
104.36.50[.]54
104.193.135[.]207
These are historical observables and should be enriched before blocking. (Anthropic)
The major campaigns this week collectively demonstrate:
- T1566: Phishing.
- T1189: Drive-by Compromise.
- T1190: Exploit Public-Facing Application.
- T1210: Exploitation of Remote Services.
- T1110: Brute Force / Password Spraying.
- T1555: Credentials from Password Stores.
- T1539 / browser-session collection: Web-session and cookie theft.
- T1055: Process Injection.
- T1053: Scheduled Task.
- T1059: Command and Scripting Interpreter.
- T1027: Obfuscated/Compressed Files and Information.
- T1071: Application Layer Protocol.
- T1090: Proxy.
- T1041/T1567: Exfiltration over C2 or web services.
- T1583/T1584: Infrastructure acquisition and compromise.
- T1595: Active Scanning.
- T1592/T1589: Gather Victim Host/Identity Information.
The emerging differentiator is not the technique IDs. It is machine-speed orchestration among them.
BlueMoon
Technical evidence: Very high.
Independent corroboration: Strong. Proofpoint and Volexity independently analyzed matching exploit code.
Attribution: Strong for established Chinese actors; weaker for temporary UNK clusters.
Disinformation likelihood: Very low.
Midnight Blizzard-aligned GTG-20006
Technical evidence: High because Anthropic observed operational workflows directly on its own platform.
Actor equivalence: Anthropic says the activity is consistent with Midnight Blizzard, not that it possesses conclusive independent government attribution.
Disinformation likelihood: Low.
Vendor-visibility caveat: Anthropic sees AI-platform behavior but not necessarily every off-platform operational event.
PRC GTG-10007
Technical evidence: High.
PRC government attribution: Unproven.
Risk of over-attribution: Moderate. Chinese origin should not automatically be equated to MSS/PLA tasking.
GTIG actor reporting
Google’s actor mappings are mature commercial-intelligence assessments supported by platform and incident-response telemetry. However, several examples describe activity observed during Q2 and are included here because the technical findings were newly disclosed during this week’s reporting window, not because every intrusion occurred this week. (Google Cloud)
1. High confidence: BlueMoon demonstrates that high-end browser exploit chains can be distributed rapidly across otherwise separate espionage clusters.
2. Moderate confidence: A centralized developer, broker, or capability-sharing channel exists behind the BlueMoon distribution pattern.
3. High confidence: AI is now operationally integrated into multiple nation-state intrusion lifecycles rather than being limited to research, lure writing, or simple code generation.
4. High confidence: Russian state-linked operators are using AI to reduce malware retooling and detection-evasion turnaround time.
5. High confidence: PRC-linked offensive ecosystems are experimenting with persistent agentic vulnerability research and autonomous exploit-development workflows.
6. High confidence: Developer environments, browser sessions, cloud identities, and authentication material are becoming more strategically useful than endpoint persistence alone.
7. Moderate to High confidence: The cost differential between elite APT teams and lower-resourced offensive actors will continue to narrow as agentic tooling absorbs repetitive technical labor.
Exploit sharing: The same advanced exploit package appears across separate actors within days.
Patch-gap weaponization: Public open-source security fixes are increasingly exploitable intelligence for adversaries before downstream stable releases reach users.
AI-driven malware mutation: Malware can now be rebuilt automatically in response to defensive detections.
AI-assisted exploit foundries: Persistent agents can perform binary analysis, hypothesis generation, exploit coding, and lab validation continuously.
Browser implants over full RATs: JungleBamboo’s LONGTALE/GemStone tradecraft shows that cookies, session tokens, screenshots, and browser data may satisfy espionage objectives without full system-level C2.
Operational AI memory: Persistent target lists, credentials, campaign state, and standing tasking allow automated operations to resume across sessions.
The critical trend is not “AI-generated malware.” It is instead, automated exploitation.

BlueMoon is an early operational example of this full chain.
A second trend is continued movement toward trusted or semi-trusted infrastructure, including:
- Cloudflare Workers and tunnels.
- Legitimate browser extensions/interfaces.
- Cloud hosting.
- AI APIs.
- Compromised hospitality providers.
- Legitimate university infrastructure.
- Public browser ecosystems.
This complicates static network blocking and increases the value of process lineage, identity telemetry, browser telemetry, and behavioral detection.
BlueMoon: Do not treat every BlueMoon user as APT31. The exploit package is shared.
UTA0560: Volexity attributes the current activity to its previously observed UTA0560 cluster with high confidence but does not publicly map it to a named PRC agency.
GTG-20006: Midnight Blizzard linkage is strong but expressed as consistency with existing public reporting rather than definitive attribution.
GTG-10007: Chinese origin and offensive intent are well established. Government control is not.
APT42/CALANQUE ION: Strong Iranian state-backed attribution.
Sandworm: Google’s SANDWORM RELIC designation should be interpreted as continuity with its established Sandworm/APT44 tracking rather than evidence of a newly formed actor.
Priority 1: Any new actor adopting BlueMoon or modified derivatives, especially outside the PRC nexus.
Priority 2: BlueMoon infrastructure and payload migration following public disclosure.
Priority 3: Evidence identifying the exploit supplier or developer behind BlueMoon.
Priority 4: New Midnight Blizzard/GTG-20006 infrastructure or malware connected to automated AI-driven evasion.
Priority 5: Continued Russian collection against Ukrainian drone manufacturers, UAV vision technologies, firmware, and supply chains.
Priority 6: PRC exploitation of network/security appliances consistent with autonomous exploit-foundry output.
Priority 7: Sandworm password-spraying and AI-themed phishing infrastructure against Ukrainian government and critical infrastructure.
Priority 8: APT42 exploitation of AI for individualized social engineering and EDR-bypass research.
Priority 9: DPRK repository poisoning, malicious developer hooks, and SOMBERMEME activity.
Priority 10: Shortening time between upstream vulnerability patches and live exploitation across open-source software ecosystems.
Conclusions
The central development this week is not a specific backdoor or a destructive cyberattack. It is a change in the economics and tempo of cyber warfare. BlueMoon shows that a sophisticated browser-to-kernel exploit chain can move across multiple espionage actors almost immediately. Anthropic’s Russian findings show that malware modification, phishing infrastructure, persistence, and collection can be delegated to AI workflows. Chinese operators are experimenting with continuous exploit foundries. Sandworm, APT42, APT24, and DPRK clusters are all integrating generative AI into existing operational models. (Proofpoint)
This does not mean autonomous AI has replaced APT operators. It means the scarce resource is shifting. Historically, the limiting factor was skilled operator time. Increasingly, the limiting factors will be target intelligence, access opportunities, high-quality vulnerabilities, infrastructure, and human decisions about what to attack. Much of the labor between those decisions can now be automated.
For defenders, that compresses the response window. The most consequential trend to monitor is therefore the transition from AI-assisted intrusion to persistent, multi-agent offensive operations capable of discovering, weaponizing, deploying, adapting, and collecting at machine speed.
如有侵权请联系:admin#unsafe.sh