MeGitLab CE/EE GraphQL Directive Code Injection VulnerabilityCVE-2026-19478 is a critical cod 2026-8-20 21:19:55 Author: horizon3.ai(查看原文) 阅读量:29 收藏
MeGitLab CE/EE GraphQL Directive Code Injection Vulnerability
CVE-2026-19478 is a critical code injection vulnerability in GitLab Community Edition (CE) and Enterprise Edition (EE). Under certain conditions, an unauthenticated remote attacker can exploit a GraphQL directive to modify or delete public projects and user data. The vulnerability has a CVSS 3.1 score of 9.4 and affects self-managed GitLab installations across multiple 18.x and 19.x release branches. Active exploitation has been observed in the wild.
Technical Details
CVE-2026-19478 is an improper control of code generation, or code injection, vulnerability involving a GraphQL directive in GitLab CE and EE.
Under certain conditions, an unauthenticated attacker can remotely exploit the vulnerability to modify or delete public projects and user data. The attack can be performed over the network, requires no privileges, and requires no user interaction. GitLab’s public disclosure does not provide the specific conditions or detailed exploitation mechanics.
The vulnerability is tracked as CWE-94 and carries a CVSS 3.1 score of 9.4 (Critical), with the vector CVSS:3.1/AV:N/AC:L/PR:N/UI:N/S:U/C:L/I:H/A:H.
GitLab.com and GitLab Dedicated are already running patched versions. Customers operating self-managed GitLab CE or EE instances within the affected version ranges should upgrade immediately.
NodeZero® Proactive Security Platform — Rapid Response
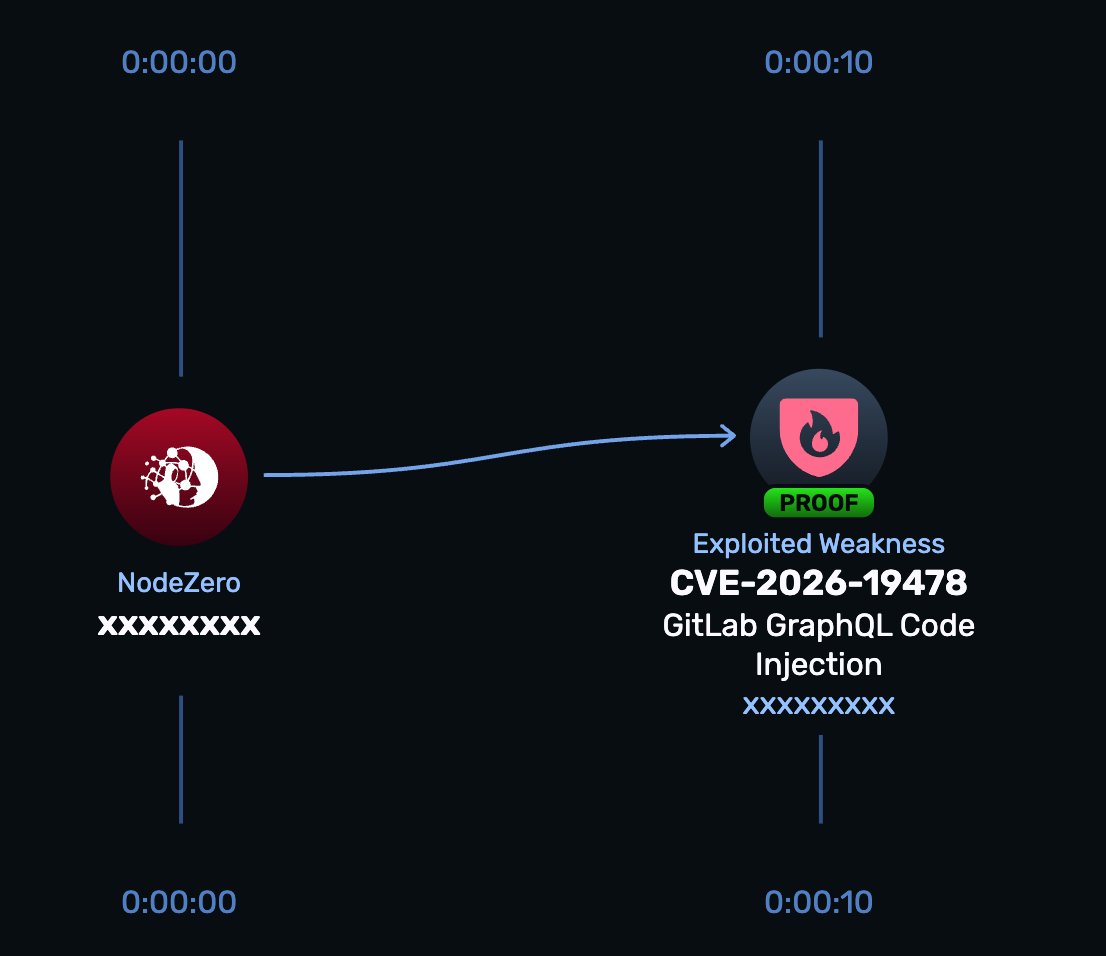
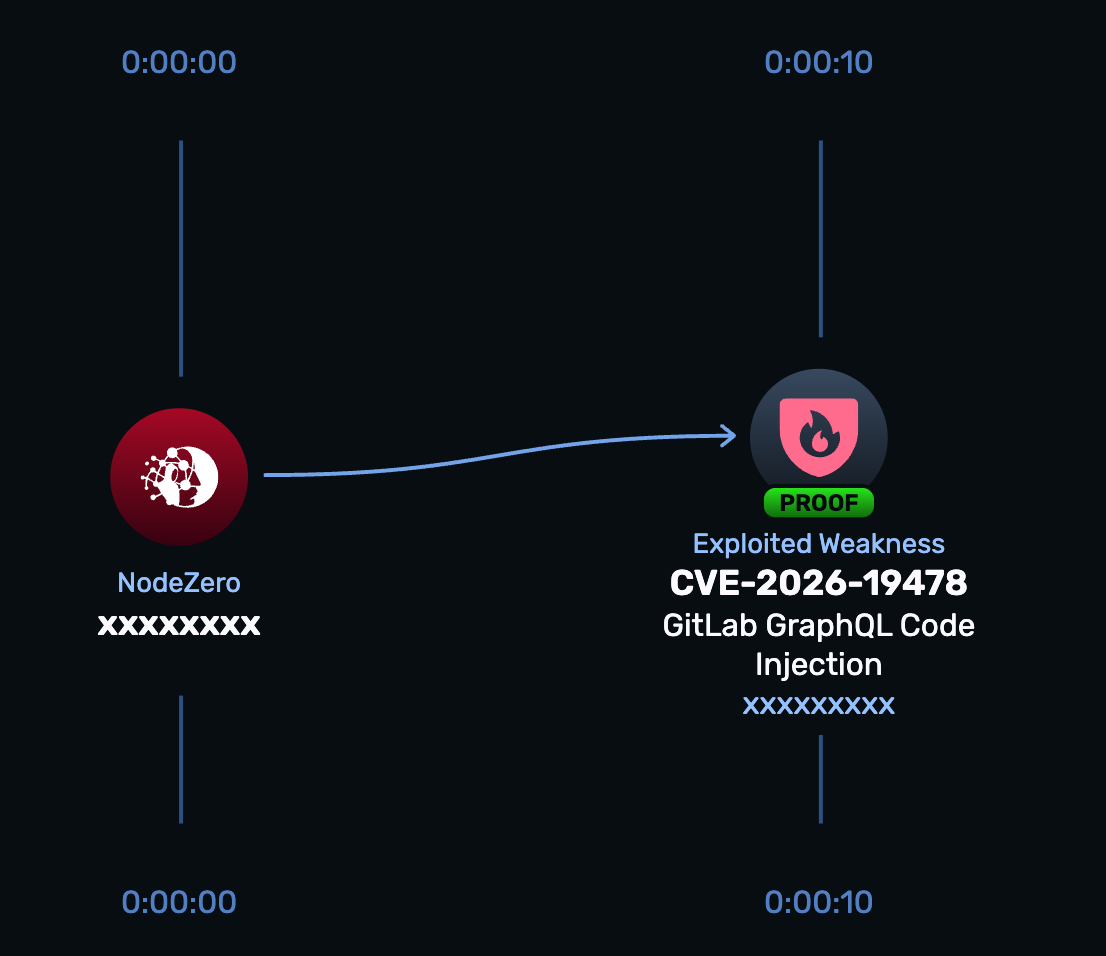
A NodeZero Rapid Response test has been developed to safely validate whether this code injection vulnerability can be exploited in your environment. The test executes real attack techniques without causing damage, giving teams immediate clarity on exposure.
- Run the Rapid Response test: Launch from the NodeZero platform to determine whether exploitation is possible
- Patch immediately: Upgrade affected self-managed GitLab instances to a fixed version
- Re-run the test: Confirm the vulnerability is no longer exploitable after remediation
Stop Guessing, Start Proving
Affected versions & patch
Affected
GitLab CE and EE:
- 18.2 before 18.11.11
- 19.0 before 19.0.8
- 19.1 before 19.1.6
- 19.2 before 19.2.4
GitLab’s CVE record identifies versions outside these ranges as unaffected.
Fixed
GitLab released fixes in:
- 18.11.11
- 19.0.8
- 19.1.6
- 19.2.4
Organizations running affected self-managed GitLab installations should upgrade immediately to the appropriate fixed version or a later supported release. GitLab.com and GitLab Dedicated were already patched and require no customer action for CVE-2026-19478.
Timeline
- August 17, 2026: GitLab released versions 18.11.11, 19.0.8, 19.1.6, and 19.2.4 and disclosed CVE-2026-19478 as a critical code injection vulnerability affecting GitLab CE and EE.
- August 20, 2026: Public reporting documented in-the-wild exploitation of CVE-2026-19478 following its disclosure.
- August 20, 2026: Horizon3.ai released a NodeZero Rapid Response test for CVE-2026-19478.
References
- GitLab Critical Patch Release: 19.2.4, 19.1.6, 19.0.8, 18.11.11
- CVE.org Record – CVE-2026-19478
- NIST NVD – CVE-2026-19478
- The Hacker News: Critical GitLab GraphQL Flaw Could Let Unauthenticated Attackers Delete Public Projects
- Dark Reading: Critical GitLab Zero-Click Flaw Poses Mitigation Challenges
Read about other CVEs
NodeZero® Platform
Implement a continuous find, fix, and verify loop with NodeZero
The NodeZero® platform empowers your organization to reduce your security risks by autonomously finding exploitable weaknesses in your network, giving you detailed guidance around how to priortize and fix them, and having you immediately verify that your fixes are effective.
Recognized By
如有侵权请联系:admin#unsafe.sh